


Penetration Testing Program
Validate Security Controls as Threat Environment Changes
Security environments do not remain static. New cloud services, remote work, application changes, infrastructure updates, acquisitions, and new threats can create exposure after a point-in-time test is complete.
HALOCK’s penetration testing program provides recurring validation so security teams can determine whether controls remain effective as the environment changes.
“HALOCK always provides a streamlined experience and good deliverables.”
– Packaging Products, Equipment Distributor and Services Organization
Reasonable Security
How HALOCK’s Penetration Testing Program Works
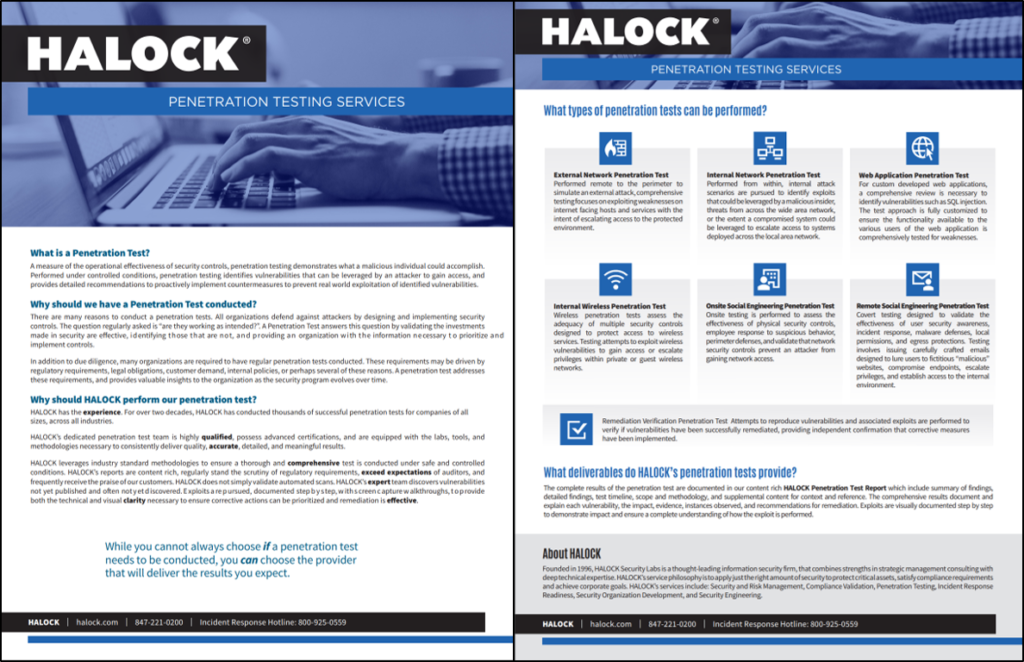
Point-in-time testing evaluates a defined environment at a specific moment. Recurring penetration testing establishes a planned cadence for reassessing networks, applications, and services based on risk, compliance requirements, material changes, or business priorities. HALOCK will partner with your team to identify and support:
- what should be tested;
- how often should testing occur;
- which assets require ongoing validation;
- what kinds of significant changes would require additional testing;
- verification of results as remediation progresses;
- Comprehensive Report: Detailed remediation plan, plus risks based on criticality.
The program can combine external, internal, wireless, web application, social engineering, adversarial, and remediation verification testing depending on the organization’s needs.
How You Benefit from Recurring Penetration Testing
A structured program helps organizations:
- identify and address new vulnerabilities sooner;
- maintain comprehensive visibility as assets and services change;
- reduce the time exploitable weaknesses remain open;
- hold technical teams accountable for remediation;
- demonstrate ongoing testing to customers, auditors, insurers, and other stakeholders;
- track improvement over time.
Recurring testing also creates continuity between assessments rather than treating each penetration test as an isolated project. Our trusted pen testing methodologies make it easier for you, harder for bad actors.

Penetration Testing and Compliance Requirements
Compliance and contractual obligations frequently require recurring testing. A program can help organizations coordinate testing schedules around requirements such as PCI DSS penetration testing, customer contracts, cyber insurance expectations, or other security obligations.
- Meet compliance obligations (PCI or client contract requirements)
- Hold technical teams accountable to remediation
- Demonstrate on-going testing to interested parties
- Proactively manage risk, resulting in fewer vulnerabilities exposed for shorter durations
HALOCK’s Penetration Testing Program can strengthen your security posture efficiently and effectively based on your timing – whether ongoing testing of many assets throughout the year or a comprehensive point-in-time test.

Why Choose HALOCK for Pen Testing?
HALOCK is committed to make sure your team is supported by decades of penetration-testing expertise with risk management and compliance experience to build programs around the organization’s actual environment.
Testing can be scheduled as recurring assessments across multiple assets or as point-in-time engagements triggered by material changes. Reports prioritize findings by criticality and provide a consistent basis for remediation, verification, and year-over-year improvement.
Our complete Offensive Security service offering includes:
External Network, Internal Network, Wireless, Web Application, Social Engineering, Assumed Breach, Adversary Simulation, Remediation Verification Pen Testing.